Here's an uncomfortable truth about running a WooCommerce store: your biggest security risk is probably something you installed yourself and then forgot about. Not a sophisticated hacker. Not a zero-day in WordPress core. A plugin. Specifically, that abandoned "quick view" plugin you added two Black Fridays ago that hasn't seen an update since.
WooCommerce powers an enormous slice of the ecommerce web, and the WordPress plugin ecosystem is one of its greatest strengths. It's also its soft underbelly. According to multiple annual vulnerability reports from the WordPress security community, the overwhelming majority of hacked WordPress sites are compromised through plugins and themes, not core. In 2023 alone, security researchers catalogued thousands of new plugin vulnerabilities, and a meaningful chunk of them affected ecommerce functionality where real money and real customer data live.
In this guide I'll walk you through exactly how to harden WooCommerce against third-party plugin attacks: how to audit what you already run, how to vet new plugins before they ever touch your production database, how to lock down the file system and admin layer, and how to monitor for the moment something slips through. I run these practices on live stores, and I'll be honest about the tradeoffs where they exist.
Key Takeaways
- Audit relentlessly. Every plugin is attack surface. Remove anything you don't actively use, and treat "deactivated" plugins as still-dangerous until deleted.
- Vet before you install. Check last-updated date, active installs, open support threads, and known CVEs before a plugin ever reaches production.
- Enforce least privilege. Restrict file editing, lock down
wp-admin, and limit which roles can install or update plugins.- Layer your defenses. A WAF, IP blocking, and file integrity monitoring catch what a single tool misses.
- Stage every update. Never update a payment-adjacent plugin directly on production without a tested rollback plan.
- Monitor continuously. The goal isn't zero incidents, it's a short detection-to-response window.
Why Third-Party Plugins Are WooCommerce's Weakest Link
WooCommerce itself is maintained by a well-resourced team and gets security attention proportional to its footprint. The problem is everything bolted onto it. A typical store I audit runs somewhere between 18 and 35 active plugins. Each one is code with database access, often running with administrator-level capabilities, written by developers of wildly varying skill and commitment.
The common attack vectors are depressingly repetitive:
- Unauthenticated SQL injection in a poorly sanitized search or filter feature.
- Arbitrary file upload flaws that let an attacker drop a PHP webshell into
wp-content/uploads. - Privilege escalation where a low-level user or unauthenticated request gains admin rights.
- Stored cross-site scripting (XSS) in product reviews, forms, or admin notices.
- Broken access control on REST API or AJAX endpoints that expose order data.
The pattern that burns most store owners is the abandoned plugin. It worked fine for years, so nobody touched it. Then a researcher publishes a vulnerability, the exploit gets weaponized within days, and automated bots start scanning the entire web for sites running that exact version. Your store doesn't need to be targeted. It just needs to be found.
Step 1: Audit Every Plugin You Already Run
Before you add a single security layer, you need an honest inventory. You cannot secure what you haven't catalogued.
Build the inventory
- Go to Plugins → Installed Plugins and export the list, or use WP-CLI with
wp plugin list --format=csvfor a cleaner output. - For each plugin, record four columns: name, version, last updated date, and do you actually use it.
- Flag anything not updated in the last 6 to 12 months. On the WordPress.org repository, the plugin page shows "Last updated" and "Tested up to." If "Tested up to" is two or more major WordPress versions behind, treat it as abandoned.
Worked example: the 29-plugin store
On a recent audit of a mid-sized apparel store, the owner had 29 active plugins. Here's how the triage shook out:
- 11 plugins were essential and well-maintained (WooCommerce, the payment gateway, Stripe, a reputable SEO plugin). Kept.
- 7 plugins did something the active theme already handled, or duplicated functionality. Removed.
- 5 plugins were deactivated but still installed. Deactivated code still sits on disk and can still be exploited through direct file access. Deleted.
- 4 plugins hadn't been updated in over 18 months. Two had known CVEs. Replaced with maintained alternatives.
- 2 plugins were "nulled" (pirated premium plugins). These are a top vector for backdoors. Removed and reinstalled from legitimate sources.
The store went from 29 plugins to 15. That's a 48% reduction in attack surface before we configured a single firewall rule. The site also loaded noticeably faster, which is a nice side benefit of ruthless auditing.
If your store relies heavily on migration or backup plugins, those deserve special scrutiny because they touch the entire database. Our guide on how to audit WordPress migration plugins for security flaws walks through that specific category in depth.
Step 2: Vet New Plugins Before They Touch Production
The cheapest security fix is the vulnerability you never install. I apply a consistent checklist before any plugin earns a place on a live store.
The pre-install checklist
- Last updated: within the last 3 to 6 months. Fresh updates signal an active maintainer.
- Active installations: higher numbers mean more eyes and faster vulnerability reporting, though popularity also attracts attackers.
- Support responsiveness: open the support forum. If recent threads sit unanswered for weeks, that's your future bug report being ignored.
- Changelog quality: a detailed changelog that mentions security fixes shows the developer takes it seriously.
- Known vulnerabilities: search the plugin slug against a public vulnerability database before installing.
- Source legitimacy: only install from the official repository, the developer's own site, or a vetted marketplace. Never from a "free premium" download site.
That last point matters more than people think. When you buy from a reputable source like the curated WordPress plugins catalog, you get code that's been vetted, versioned, and backed by a vendor who has a reputation to protect. A pirated copy of the same plugin may carry an injected payload that phones home or opens a backdoor.
Test in staging, always
Spin up a staging copy that mirrors production. Install the candidate plugin there, run it for a few days, and watch for unexpected outbound requests, new admin users, or modified core files. Only promote to production once it's clean. If you want a sandbox on your own machine for testing Windows-based admin tooling alongside your dev environment, our rundown of running Windows apps on a Mac with a VM covers the isolation options.
Step 3: Lock Down the File System and Admin Layer
Even a well-vetted plugin can turn out to have a flaw. Your job is to limit the blast radius when it does. These are the hardening measures that pay off repeatedly.
Disable the file editor
WordPress ships with a built-in plugin and theme code editor accessible from the admin. If an attacker gets admin access, that editor hands them instant code execution. Disable it by adding this to wp-config.php:
define( 'DISALLOW_FILE_EDIT', true );
Restrict PHP execution in uploads
The wp-content/uploads directory should hold images and documents, never executable PHP. Block PHP execution there at the server level. On Apache, drop an .htaccess into the uploads folder that denies access to .php files. On Nginx, add a location block that returns 403 for PHP in that path. This single rule neutralizes a huge class of file-upload exploits.
Enforce least privilege
- Give each team member the lowest role that lets them do their job. Order fulfillment staff rarely need administrator access.
- Limit who can install and update plugins to one or two trusted admins.
- Use strong, unique passwords and enforce two-factor authentication on every admin account.
While we're on the subject of credential hygiene, if your team is still sharing a password in a spreadsheet, read how to safely switch password managers without losing data and fix that this week.
Protect the admin and login endpoints
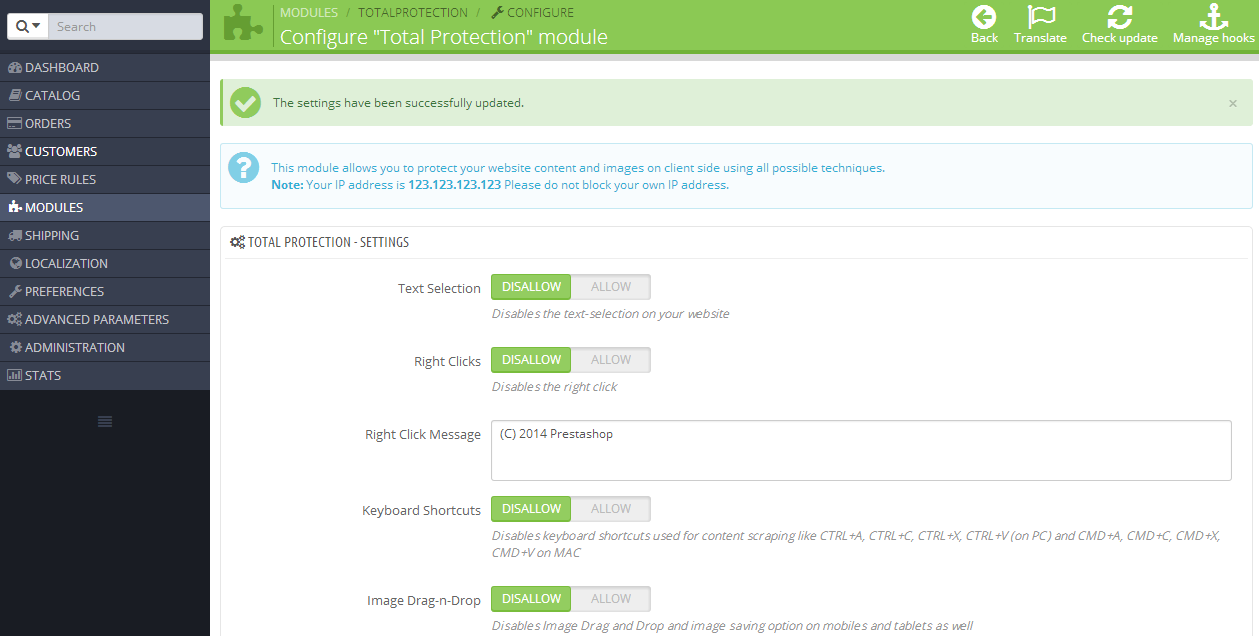
Brute-force bots hammer wp-login.php and the XML-RPC endpoint constantly. Rate-limit login attempts, and consider blocking traffic from regions where you have no customers. A tool like WordPress IP Blocker Pro lets you block individual addresses, ranges, and entire countries, which dramatically cuts the automated noise hitting your login and REST endpoints.
Step 4: Add Layered Protection with Dedicated Security Tools
No single tool catches everything. Defense in depth means stacking complementary layers so a miss in one is caught by another. Here's how the main categories compare.
| Protection Layer | What It Stops | Catches Zero-Days? | Setup Effort | Best For |
|---|---|---|---|---|
| Web Application Firewall (WAF) | SQLi, XSS, malicious requests | Partially (via rules) | Medium | Blocking exploit attempts in real time |
| IP / Country Blocking | Brute force, bot scanning | No | Low |